SMB Tech & Cyber Newsletter | CPF Coaching
I empower Chief Information Security Officers (CISOs) and Small to Medium-sized Businesses (SMBs) to elevate their cybersecurity strategies, guiding them past stagnation to achieve tangible outcomes.
CPF Coaching | Christophe Foulon
Show overview
SMB Tech & Cyber Newsletter | CPF Coaching has been publishing since 2022, and across the 4 years since has built a catalogue of 132 episodes. That works out to roughly 20 hours of audio in total. Releases follow a fortnightly cadence.
Episodes typically run under ten minutes — most land between 3 min and 11 min — with run-times ranging widely across the catalogue. None of the episodes are flagged explicit by the publisher. It is catalogued as a EN-language Business show.
The show is actively publishing — the most recent episode landed earlier today, with 15 episodes already out so far this year. The busiest year was 2024, with 38 episodes published. Published by CPF Coaching | Christophe Foulon.
From the publisher
I empower Chief Information Security Officers (CISOs) and Small to Medium-sized Businesses (SMBs) to elevate their cybersecurity strategies, guiding them past stagnation to achieve tangible outcomes. substack.cpf-coaching.com
Latest Episodes
View all 132 episodesTrust the Input? False Fronts, Agentic Privacy, and Intelligent Interfaces
Who Answers When Your AI Agent Breaks the Law
Four Exploited Flaws and One Persistent Agent Problem
Why SMBs Need a Cyber Control Loop: CISA, Labcorp, and AI Risks
Evidence Before Authority: Securing SMB Tech and AI Systems
This Week's SMB Risk Signals: Patch the VPN Edge, Audit Broker Data, and Tier AI Work
The Top 3 Unmanaged Risks Threatening Your SMB Right Now
SMB Risk Briefing: Lock the Controllers, Unify the Evidence, and Modernize AI with Real Ownership
This Week's SMB Risk Signals: Router Hygiene, Genetic Data, and Agentic AI
Can Your Security Tools, Cameras, and Agents Prove Their Work?
SMB Cyber Risk: Securing the Control Plane and Agentic AI
Stolen Logins, AI Agents, and $450K Regulatory Fines
5 Critical Security Alerts from Last Week: Copilot Bugs, Bluetooth Hacks, and New Privacy Laws
January 2026 Alert: Critical Microsoft Copilot vulnerability (Reprompt), Bluetooth "WhisperPair" exploit affecting Sony/Google devices, and new privacy laws in IN, KY, & RI. Get the executive summary and 30-day mitigation plan for SMBs. This is a public episode. If you'd like to discuss this with other subscribers or get access to bonus episodes, visit substack.cpf-coaching.com/subscribe
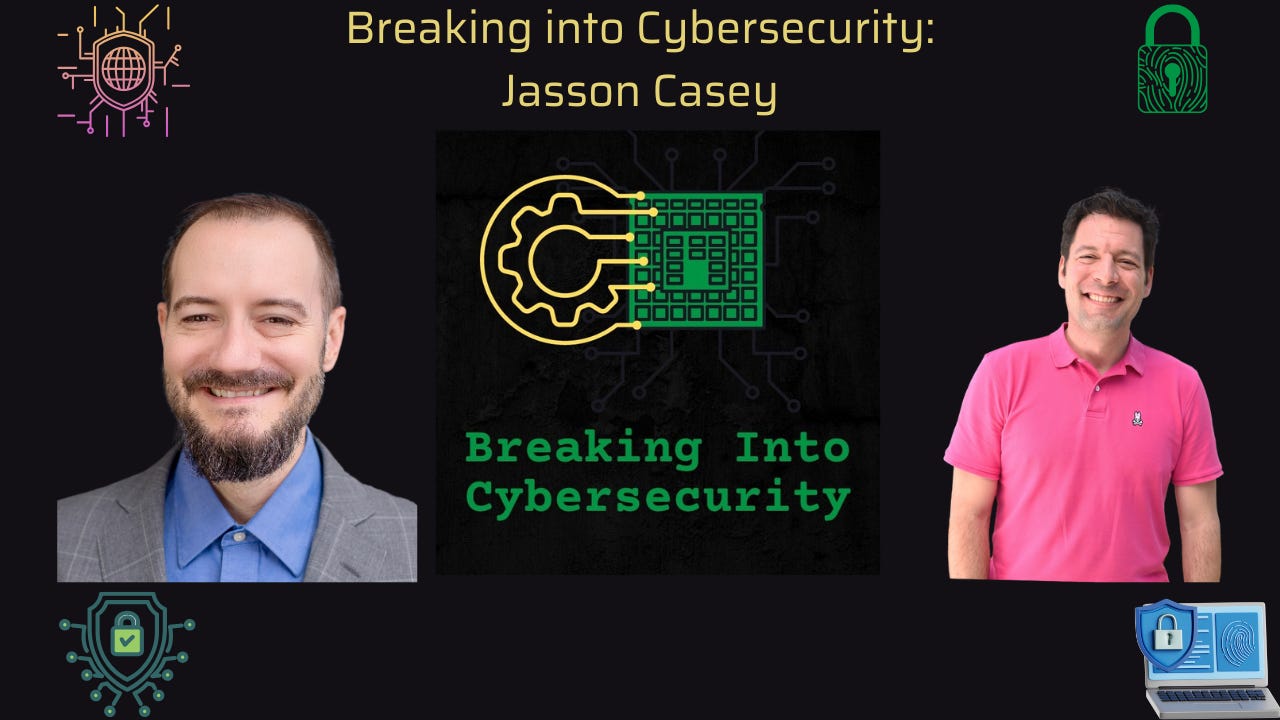
AI, Identity, and Breaking Into Cyber: CEO Jasson Casey’s Blueprint for Success
From building software to defending it: Jason Casey (CEO, Beyond Identity) shares his journey from Software Engineer to Cybersecurity Expert. Discover why mastering network protocols and engineering fundamentals is the secret to a successful cyber career. Listen now on Breaking into Cybersecurity. This is a public episode. If you'd like to discuss this with other subscribers or get access to bonus episodes, visit substack.cpf-coaching.com/subscribe
The Glass House: Why 2026 is the Year We Must Audit Our "Agents" and "Avatars"
CES 2026 changed the threat landscape. From "Superuser" AI agents to "cute" surveillance robots like Mirumi, we outline the top 4 trends SMB tech leaders must address immediately to secure their organizations. This is a public episode. If you'd like to discuss this with other subscribers or get access to bonus episodes, visit substack.cpf-coaching.com/subscribe
3 Urgent Cyber Threats Costing SMBs Millions (2025 Update)
Urgent briefing for US SMBs: Critical patches needed for WatchGuard, Fortinet, & Cisco. Discover how to stop AI attacks and avoid $3M breach costs. Read the Urgent briefing for US SMBs: Critical patches needed for WatchGuard, Fortinet, & Cisco. Discover how to stop AI attacks and avoid $3M breach costs. Read the plan. This is a public episode. If you'd like to discuss this with other subscribers or get access to bonus episodes, visit substack.cpf-coaching.com/subscribe
Don't Boil the Ocean: A Cost-Effective Architecture for CMMC Level 2
CMMC Phase 1 is effective as of Nov 2025. DIB leaders: Get the strategic guide to CUI, VDI, and NIST 800-171 compliance before the 2026 deadline. This is a public episode. If you'd like to discuss this with other subscribers or get access to bonus episodes, visit substack.cpf-coaching.com/subscribe
The Silent Kill Switch: Why Your Business Needs a "Human" Disaster Recovery Plan
Is your business one tragedy away from collapse? Learn how to mitigate "Key Person Risk" and the "Bus Factor" with our 2025 guide to IT succession planning. This is a public episode. If you'd like to discuss this with other subscribers or get access to bonus episodes, visit substack.cpf-coaching.com/subscribe
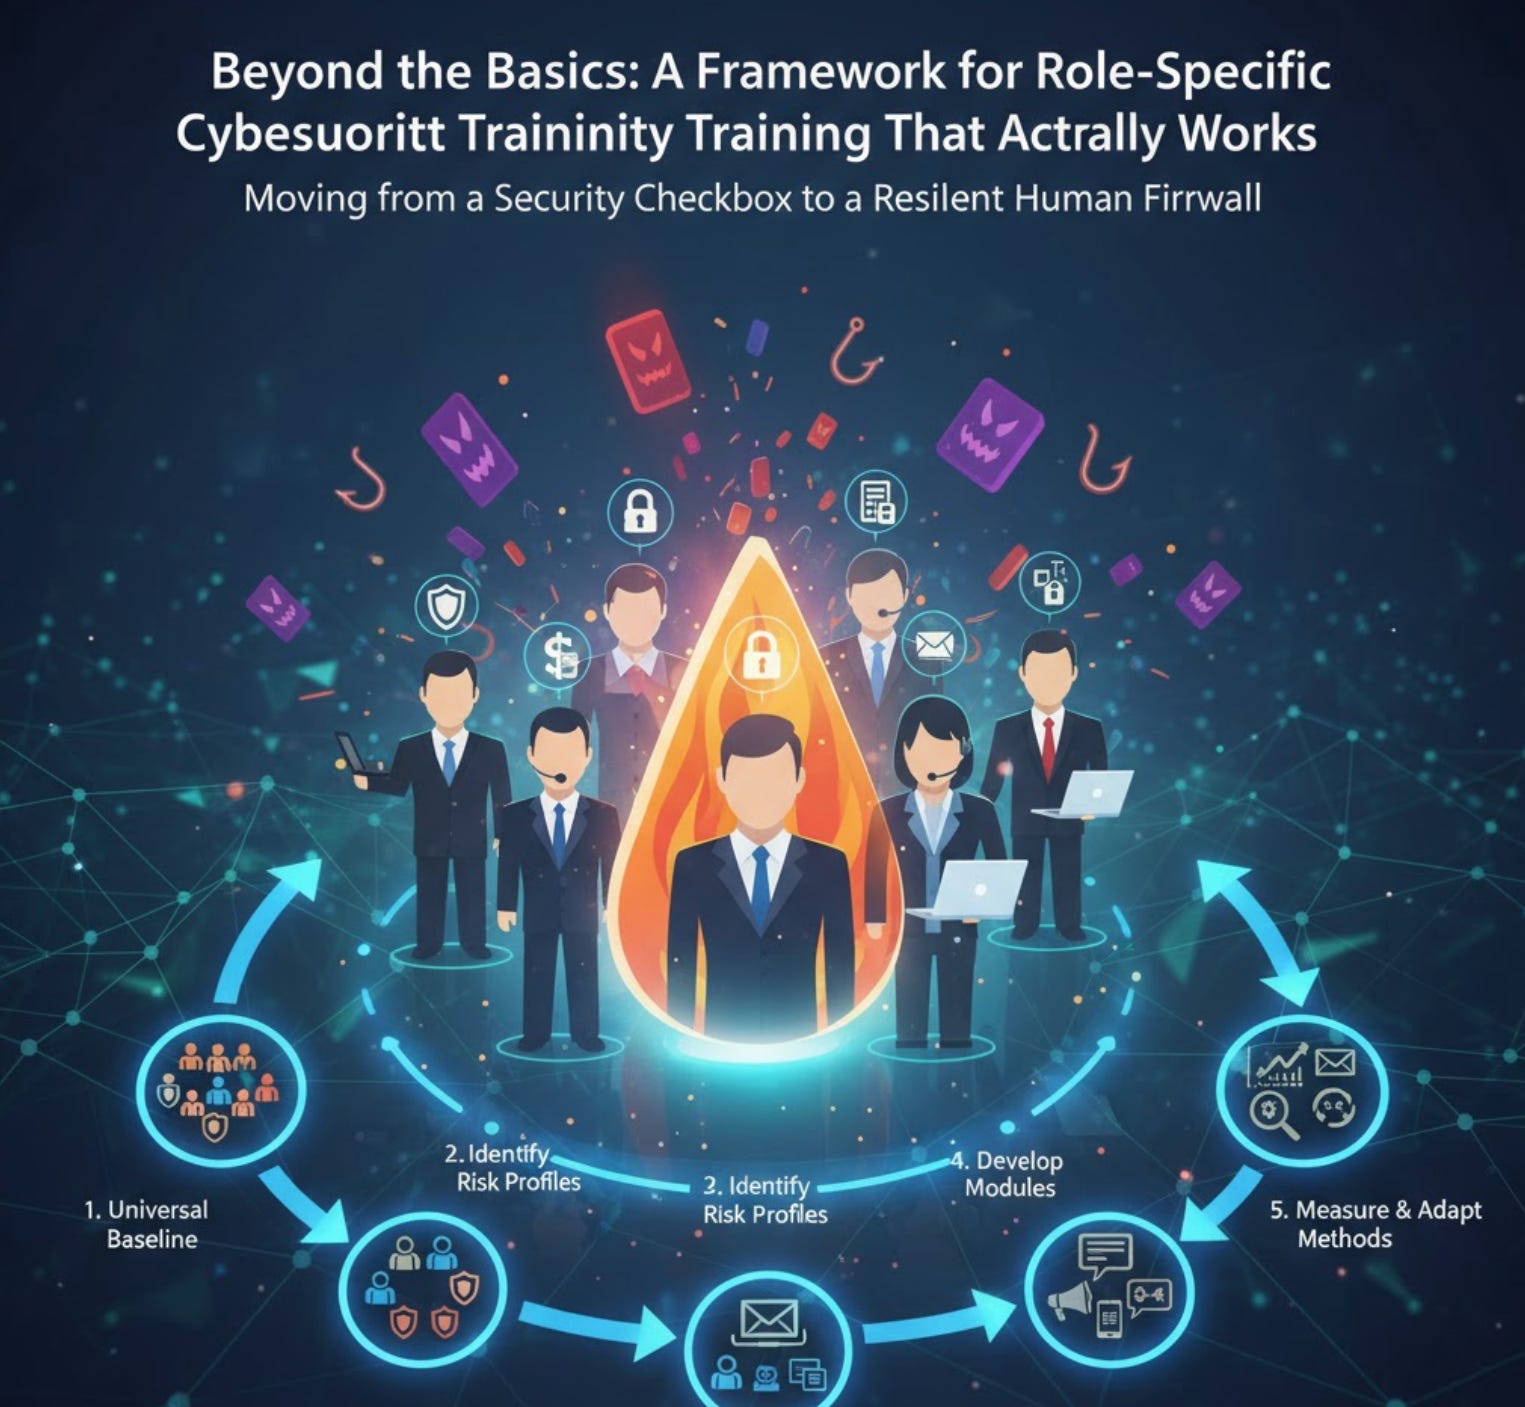
Your CEO and Your Sales Team Don't Face the Same Threats.
The “One-Size-Fits-All” ProblemWe’ve all been there. A mandatory, hour-long cybersecurity training video that covers everything from phishing to physical security in a bland, generic way. Your marketing team is half-listening while thinking about their next campaign, and your finance department is wondering how any of this applies to their daily invoice processing. This is a public episode. If you'd like to discuss this with other subscribers or get access to bonus episodes, visit substack.cpf-coaching.com/subscribe
Breaking into Cybersecurity: An In-Depth Conversation with Eric Stride
In the latest episode of “Breaking into Cybersecurity,” host Chris Foulon sits down with Eric Stride, the Chief Security Officer at Huntress. Eric’s journey into cybersecurity is not only inspiring but also enlightening for anyone looking to enter this ever-evolving field. With over two decades of experience in the military and private sectors, Eric shares his insights on career development, leadership, and the future of cybersecurity. This is a public episode. If you'd like to discuss this with other subscribers or get access to bonus episodes, visit substack.cpf-coaching.com/subscribe