
Open Source Security
554 episodes — Page 6 of 12

Ep 303Episode 303 - Log4j Christmas Spectacular!
Josh and Kurt start the show with the reading of a security themed Christmas poem. We then discuss some of the new happenings around Log4j. The basic theme is that even if we were over-investing in Log4j, it probably wouldn't have caught this. There are still a lot of things to unpack with this event, I'm sure we'll be talking about it well into the future. Log before Christmas poem 'Twas the night before Christmas, when all through the stack Not a scanner was scanning, not even a rack, The SBOMs were uploaded to the portal with care, In hopes that next year would be boring and bare The interns were nestled all snug at their beds; While visions of dashboards danced in their heads; The CISO in their 'kerchief, and I in my cap, Had just slept our laptops for a long winter's nap, When all of a sudden the pager went ack ack I sprang to my laptop with worries of attack Away to the browser I flew like a flash, Tore open the window and cleared out the cache The red of the dashboard the glow of the screen Gave a lustre of disaster my eyes rarely seen When what to my wondering eyes did we appear, But a new advisory and eight vulnerabilities to fear, Like a little old hacker all ready to play, I knew in a moment it must be Log4j More rapid than gigabit its coursers they came, And it whistled, and shouted, and called them by name: "Now, Log4Shell! now CVE! now ASF and NVD! On, CISA! on, LunaSec! on, GossiTheDog! To the top of the HackerNews! to the top of the wall! Now hack away! hack away! hack away all!" Like the bits that before the wild CDN fly by When they meet with a firewall, they mount to the sky; So up to the cloud like bastards they flew With tweets full of vulns, and Log4j too— And then, in a twinkling, I read in the slack The wailing and screaming of each analyst called back As I drew in my head, and was turning around, Down the network Log4j came with a bound. It was dressed in a hoodie, black and zipped tight, The clothes were all swag from a conference one night A bundle of vulns it had checked in its git And it looked like a pedler just being a twit The changelog—how it twinkled! its features, how merry! Its versions were like roses, its logo like a cherry! Its droll little mouth was drawn up like an at, And the beard on its chin made it look stupid and fat The stump of a diff it held tight in its teeth, And the bits, they encircled the repo like a wreath; It had a flashy readme an annoying little fad That shook when it downloaded, like a disk drive gone bad It was chubby and plump, an annoying old package, And I laughed when I saw it, in spite of the hackage A wink of its bits and a twist of its head Soon gave me to know I had everything to dread It spoke not a word, but went straight to its work, And pwnt all the servers; then turned with a jerk, And laying its patches aside of its nose, And giving a nod, up the network it rose; It sprang to its packet, to its team gave them more, And away they all fled leaving behind a back door But I heard it exclaim, ere it drove out of sight— "Merry Christmas you nerds, Log4j won tonight!"

Ep 302Episode 302 - Log4j is a mess
Josh and Kurt talk about the same topic everyone is talking about, Log4j. This episode was recorded on the Wednesday after the first Log4j issue. We point out all the gaps and difficulties for the defenders. The situation has gotten worse since then. Good luck to everyone dealign with this thing Show Notes Log4j GSD entry Minecraft server discussion Log4j GitHub issue 608

Ep 301Episode 301 - You're holding it wrong: the importance of unlearning
Josh and Kurt talk about the epic failure that was episode 300. But this ties nicely into the topic of the day which is new ways to do things. The example is a new way to hold a controller when playing Tetris. There are always new tools and new ideas in security. Sometimes we have to abandon the old way because the new way to too good to ignore. Show Notes Lawfare Apple NSO podcast New way to play Tetris

Ep 300Episode 300 - Apple vs NSO: What can copyright do for you?
the lawsuit is based on CFAA, not on copyright. We apologize for this enormous oversight. Josh and Kurt talk about Apple suing NSO using a copyright claim as their vehicle. Copyright is often used as a reason to bring lawsuits, even when it doesn't always make sense. Copyright has been used by open source to expand rights, and many companies to restrict rights. It's a very odd law sometimes. At the end of the day it seems the only real path forward for a problem like NSO is up to governments to protect their citizens. Show Notes Apple sues NSO group VMWare EULA

Ep 299Episode 299 - Experts From A World That No Longer Exists
Josh and Kurt talk about an article about how expertise has a limited lifetime. We are all experts in something, but some of us will find our expert knowledge to be outdated eventually. We discuss what that means in the context of security and tech and disagree about how to best keep your skills up to date. Show Notes Experts From A World That No Longer Exists Neuroplasticity Scotty and the mouse Git 2.34 4H Public Speaking

Ep 298Episode 298 - David A Wheeler discusses the OpenSSF
Josh and Kurt talk to David A. Wheeler about everything OpenSSF. The Open Source Security Foundation is part of the Linux Foundation, and there are 6 OpenSSF working groups. David does a great job explaining how the OpenSSF works and what the 6 working groups are doing. The working group are (in no particular order): Identifying Security Threats, Security Tooling, Best Practices, Vulnerability Disclosures, Digital Identity Attestation, Securing Critical Projects. Show Notes David A Wheeler Episode 14 – David A Wheeler: CII Badges Sigstore joins the OpenSSF OpenSSF Technical Working Groups NPM requires MFA LISH Backstabber's Knife Collection: A Review of Open Source Software Supply Chain Attacks

Ep 297Episode 297 - 25 years of smashing stacks, fun, and profit
Josh and Kurt talk about the famous Phrack 49 article "Smashing the Stack for Fun and Profit" turning 25 years old. This paper created a massive amount of change in the industry, possibly more than any other paper ever written. Everything from making exploiting stack overflows easier, to defenders creating technologies such as stack canaries are the direct result of this work. Show Notes Phrack 49 Kurt's Interview with Elias Levi aka Aleph One

Ep 296Episode 296 - Is Trojan Source a vulnerability?
Josh and Kurt talk about the new Trojan Source bug. We don't always agree on if this is a vulnerability (it's not), but by the end we come to an agreement that ASCII is out, Unicode is in. We don't live in a world where you can make a realistic suggestion to return to using only ASCII. There are a lot of weird moving parts with this one. Show Notes Trojan Source oss-security message GitHub example

Ep 295Episode 295 - Open source security isn't free
Josh and Kurt talk about Josh's electric car and new job. We then talk about the recent UAParser.js malware incident. There have been a lot of calls to do more to secure open source, but nobody seems to have any concrete proposals or suggestions to fund any of these activities. Show Notes UAParser.js CISA announcement

Ep 294Episode 294 - Chris Wysopal on the state of security education
Josh and Kurt talk to Chris Wysopal, AKA Weld Pond, about security education. We talk about the current state of how we are learning about security as students and developers. What the best way to get developers interested in learning more about security? We end the show with fantastic advice from Chris for anyone new to the field of technology or security. Show Notes Chris Wysopal Veracode l0phtcrack
Ep 293Episode 293 - Scoring OpenSSF Security Scoring
Josh and Kurt talk about the release of OpenSSF Security Scorecards version 3. This is a great project that will probably make a huge difference. Most of the things the scorecards are measuring are no brainier activities. We go through the list of metrics being measured. There are only a few that we don't think are fantastic. Show Notes 4 of spades OpenSSF Chris Montgomery audio explanation Scorecard 3.0.0 Scoring criteria Python Skeleton

Ep 292Episode 292 - Apache RCE and Twitch epic pwn
Josh and Kurt talk about the recent Twitch hack and how in the modern age leaking source code almost certainly doesn't matter. The leaked data however is a big deal. We also discuss a recent Apache httpd update. Some things went right, some things went wrong. Dealing with vulnerabilities is hard. Show Notes Parasocial Relationship Twitch Hack Soviet B-29 Clone Apache CVE Apache Advisory GossiTheDog Tweet Hacker Fantastic exploit

Ep 291Episode 291 - Everyone sucks at vulnerability disclosure
Josh and Kurt talk about recent events around Apple and Microsoft disclosing security vulnerabilities. Microsoft usually does a good job, but Apple has a long history of not having a great bug bounty or vulnerability disclosure policy. None of this is simple, but hopefully you'll have some fun and learn a bit about the whole vulnerability disclosure process. Show Notes Apple 0days Microsoft Exchange flaw THIS IS HOW THEY TELL ME THE WORLD ENDS Linux Foundation Vulnerability Disclosure Timezone problem

Ep 290Episode 290 - The security of the Matrix
Josh and Kurt talk about the security of the Matrix movie series. There was a new Matrix trailer that made us want to discuss some of the security themes. We talk about how the movie is very focused on computing in the 90s. How Neo probably ran Linux and they used a real ssh exploit. How a lot of the plot is a bit silly. It's a really fun episode. Show Notes Matrix 4 trailer nmap in the Matrix VFX Artists react to the Mandalorian Glasshouse Universal Paperclips

Ep 289Episode 289 - Who left this 0day on the floor?
Josh and Kurt talk about an unusual number of really bad security updates. We even recorded this before the Azure OMIGOD vulnerability was disclosed. It's certainly been a wild week with Apple and Chrome 0days, and a Travis CI secret leak. Maybe this is the new normal. Show Notes Matrix 4 trailer Travis CI issue Apple 0day patches Chrome 0day patches CGP Grey Where is the European Union

Ep 288Episode 288 - Linux Kernel compiler warnings considered dangerous
Josh and Kurt talk about some happenings in the Linux Kernel. There are some new rules around how to submit patches that goes against how GitHub works. They're also turning all compiler warnings into errors. It's really interesting to understand what these steps mean today, and what they could mean in the future. Show Notes The Register Linux story OpenSSL Release Notes

Ep 287Episode 287 - Is GitHub's Copilot the new Clippy?
Josh and Kurt talk about GitHub Copilot. What can we learn from a report claiming 40% of code generated by Copilot has security vulnerabilities? Is this the future or just some sort of strange new thing that will be gone as fast as it came? Show Notes GitHub Copilot Copilot research paper

Ep 286Episode 286 - Open source supply chain with Google's Dan Lorenc
Josh and Kurt talk to Dan Lorenc from Google about supply chain security. What's currently going on in this space and what sort of new thing scan we look forward to? We discuss Google's open source use, Project Sigstore, the SLSA framework and more. Show Notes Dan's Twitter Sigstore SLSA Framework
Ep 285Episode 285 - Open source owes you nothing!
Josh and Kurt talk about open source bugs. What happens if a project decides to close most of their bugs? Nothing really. Bug trackers aren't a help desk. Show Notes Emacs closes 45% of bugs UVI Tesla investigation UK COVID spreadsheet

Ep 284Episode 284 - What happens when we DRM power tools?
Josh and Kurt talk about a Home Depot plan to put DRM on power tools. Anyone can add a computer to anything for a few dollars now. How secure is any of this. What does it mean when the things we buy start to acquire DRM? There are a lot of new questions we don't have any real answers for. Show Notes Home Depot power tools Ray Ozzie's IoT board First-sale doctrine
Ep 283Episode 283 - When vulnerability disclosure becomes dangerous
Josh and Kurt talk about a very difficult disclosure problem. What happens when you have to report a vulnerability to an ethically questionable company? It's less simple than it sounds, many of the choices could end up harming victims. Show Notes Disclosure Dilemmas @evacide Bob Diachenko This Is How They Tell Me The World Ends

Ep 282Episode 282 - The security of Rust: who left all this awesome in here?
Josh and Kurt talk about a story from Microsoft declaring Rust the future of safe programming, replacing C and C++. We discuss how tooling affects progress and why this isn't always obvious when you're in the middle of progress. Show Notes Microsoft: Rust Is the Industry's 'Best Chance' at Safe Systems Programming Josh's devopsdays talk Microsoft moved font handling out of the kernel Atari 2600 emulator in Minecraft Rate of technology adoption

Ep 281Episode 281 - If you spy on journalists, you're the bad guys
Josh and Kurt talk about the news that the NSO Group is widely distributing spyware onto a large number of devices. This news should be a wake up call for anyone creating devices and systems that could be attacked, it's time to segment services. There's not a lot individuals can do at this point, but we have some ideas at the end of the episode. Show Notes NSO Group spying Technical details Twitter thread Are we the Baddies?
Ep 280Episode 280 - The perils of Single Sign On
Josh and Kurt talk about what happens when you lose access to your Single Sign On provider. These providers have become critical to many of us, if we lose access to our SSO account we will lose access to many services. Show Notes Postbank

Ep 279Episode 279 - The audacity of Audacity: When open source goes rogue
Josh and Kurt talk about the events happening to the Audacity audio editor. What happens if a popular open source application is acquired by an unknown entity? Can this happen to other open source projects? What can we do about it? Show Notes SGDQ Paper Mario Paper Mario Arbitrary Code Execution explained Freenode Audacity acquired by Muse Group Audacity fork

Ep 278Episode 278 - Could SELinux have stopped SolarWinds?
Josh and Kurt talk about a listener provided question. Could SELinux have stopped the SolarWinds attack? Given what we know, the answer is technically yes, but practically no. SELinux is awesome, but it's very difficult to sandbox something like a build system. Show Notes Gone in 60 milliseconds
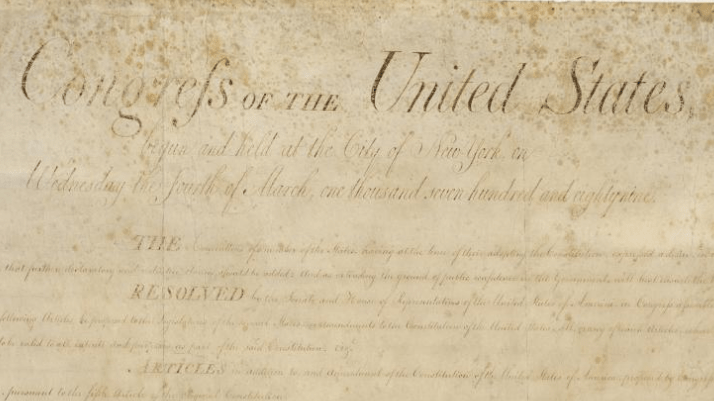
Ep 277Episode 277 - Privacy and activism with Chris Weiland
Josh and Kurt talk to Chris Weiland from Restore the Fourth Minnesota. Restore The Fourth Minnesota is nonprofit dedicated to restoring the Fourth Amendment to the U.S. Constitution and ending unconstitutional mass government surveillance. Chris drops a ton of knowledge about how to be an effective tech activist, what his group is doing, and most importantly we get actionable advice! Show Notes Restore the Fourth Minnesota Restore the Fourth Minnesota on Twitter Writ of assistance Carpenter vs United States How many US federal laws are there? Restore the Fourth Episode 114 – Review of "Click Here to Kill Everybody" EFF EFA ACLU affiliates Glenn Greenwald TED talk
Ep 276Episode 276 - Security, behavior, and the environment
Josh and Kurt talk about how our environment affects our behavior, and in turn our level of security. We often ignore what's happening around us when everything is related. Show Notes Judges more lenient after a break Dungeons and Data Poverty changes your DNA

Ep 275Episode 275 - What in the @#$% is going on with ransomware?
Josh and Kurt talk about why it seems like the world of ransomware has gotten out of control in the last few weeks. Every day there's some new and more bizarre ransomware story than we had yesterday. Show Notes Spurious Correlations Ransom recovered Adam Shostack Ransomware is not the problem Latvian Woman charged for writing ransomware
Ep 274Episode 274 - Mr. Amazon's Neighborhood
Josh and Kurt talk about Amazon sidewalk. There is a lot of attention, but how is this any different than the surveillance networks Apple and Google have built? Show Notes Amazon Sidewalk Ads and toothpaste Airtags and stalking
Ep 273Episode 273 - Can we stop the coming artificial unintelligence deluge?
Josh and Kurt talk about AI driven comments. We live in a world of massive confusion and disruption where what is true and false, real and fake, are often widely debated. As AI grows and evolves what does it mean for this future? We don't really have any answers, but we ask a lot of questions. This isn't easy, nor will it be solved quickly, but solving it is not optional. Show Notes AIs and Fake Comments ACLU AMA Cloudflare Cryptographic Attestation of Personhood Evil bit Boris Johnson Painting Buses
Ep 272Episode 272 - The Biden Cybersecurity Executive Order
Josh and Kurt talk about the Biden Administration new cybersecurity executive order. There are some good ideas in there, but at the end of the day it's an unfunded mandate. Unfunded mandates are difficult to implement. Show Notes Biden Executive Order Fact Sheet Obama's cyber EO

Ep 271Episode 271 - Pipeline security: There is no problem humans can't make worse
Josh and Kurt talk about how people handle problems. We open with the story of the Colonial Pipeline hack, but then go into some of the ways people tend to make problems worse. Show Notes Male vs Female trees Pipeline hack XKCD Pipelines TSA Pipeline Security
Ep 270Episode 270 - Hello dark patterns my old friend
Josh and Kurt talk about dark patterns. A dark pattern is when a service tries to confuse a user into doing something they don't want to, like unknowingly purchasing a monthly subscription to something you don't need or want. The US Federal Trade Commission is starting to discuss dark patterns in webs sites and apps. Show Notes Dark Patterns Types of Dark Patterns FTC Bringing Dark Patterns to Light LTT Dell Warranty

Ep 269Episode 269 - Do not experiment on the Linux Kernel
Josh and Kurt talk about the University of Minnesota experimenting on the Linux Kernel. There's a lot to unpack in this one, but the TL;DR is you probably don't want to experiment on the kernel. Show Notes Linux Bans University of Minnesota for Sending Buggy Patches in the Name of Research University of Minnesota security researchers apologize for deliberately buggy Linux patches The International Obfuscated C Code Contest
Ep 268Episode 268 - Can we trust any 3rd parties?
Josh and Kurt talk about what 3rd party means in the current world. From 5G suppliers, to the Codecov and Solarwinds breaches. Is there anyone we can trust? Show Notes Europe and 5G Codecov Codecov Reuters story Red Hat OpenSSH advisory
Ep 267Episode 267 - Does 0day still mean 0day?
Josh and Kurt talk about 0day security vulnerabilities. What are they? What were they? And why the name has taken on a new meaning, and that's OK. Show Notes Hacker History Podcast Chrome 0day NTFS Documentation
Ep 266Episode 266 - The future of security scanning with Debricked
Josh and Kurt talk to Emil Wåreus from Debricked about the future of security scanners. Debricked is doing some incredibly cool things to avoid relying on humans for vulnerability identification and cataloging. Learn what the future of security scanning is going to look like. Show Notes Debricked Emil's Linkedin
Ep 265Episode 265 - The lies closed source can tell, open source can't
Josh and Kurt talk about the PHP backdoor and the Ubiquity whistleblower. The key takeaway is to note how an open source project cannot cover up an incident, but closed source can and will cover up damaging information. Show Notes PHP backdoor Ubiquity coverup 3D printed TSA keys LockPickingLaywer Determining Key Shape from Sound Lock camera
Ep 264Episode 264 - DevSecOps with GitLab's Mark Loveless
Josh and Kurt talk to Mark Loveless from GitLab. We touch on DevSecOps, what GitLab is doing, threat modeling, and the time Mark tested positive for TNT at the airport. It's a great conversation. Show Notes Mark Loveless Twitter GitLab GitLab Handbook How we approach open source security PASTA threat modeling GitLab security features Tales from the Past - "You Tested Positive for TNT"

Ep 263Episode 263 - GitHub pulls exploits, LinuxFoundation sign all the things
Josh and Kurt talk about how terrible daylight savings is. GitHub yanking some exploit code. And the Linux Foundation new project to sign all the things. Show Notes Researcher Publishes Code to Exploit Microsoft Exchange Vulnerabilities on Github GitHub content restrictions Reproducing the Microsoft Exchange Proxylogon Exploit Chain

Ep 262Episode 262 - A discussion with Loris and Pop from Sysdig
Josh and Kurt talk to Loris Degioanni and Dan from Sysdig. Sysdig are the minds behind Falco, an amazing open source runtime security engine. We talk about where their technology came from, they huge code donation to the CNCF and what securing a modern infrastructure looks like today. Show Notes Sysdig Falco Loris' Twitter Dan "Pop" Popandrea's Twitter Sysdig contributes Falco's kernel module, eBPF probe, and libraries to the CNCF pdig Sysdig 2021 container security and usage report: Shifting left is not enough
Ep 261Episode 261 - DWF is back! Welcome to community powered CVE
Josh and Kurt talk about DWF. It's back and the intention is to have real community driven security identifiers! Show Notes Committee vs Community dwflist repo dwf-request tooling repo dwf-workflow policy repo CVE plateua graph iwantacve.org

Ep 260Episode 260 - Dave Jevans tells us what CipherTrace is up to
Josh and Kurt talk with Dave Jevans CEO of CipherTrace and chairman of the anti-phishing working group about the challenges of keeping track of cryptocurrency in the modern age. Show Notes Dave's Twitter CipherTrace Anti Phishing Working Group

Ep 259Episode 259 - What even is open source anymore?
Josh and Kurt talk about the question "what is open source?" Why do we think it's broken today, and what sort of ideas about what should come next. Show Notes OSI Bruce Perens Post Open Source Josh's community blog post Corey Doctorow Uber Twitter thread
Ep 258Episode 258 - Stop using C
Josh and Kurt talk about the Google Project Zero report titled "A Year in Review of 0-days Exploited In-The-Wild in 2020". It's a cool report but we don't agree on the conclusion. The answer isn't to security harder, it's to stop using C. Show Notes Google Project Zero Year of 0-days Kurt's CUPS tweet
Ep 257Episode 257 - The sudo and libgcrypt vulnerabilities
Josh and Kurt talk about the recent sudo and libgcrypt security vulnerabilities. What's the deal with these buffer overflows and TOCTU bugs? Show Notes Sudo buffer overflow Sudo SELinux bug libgcrypt buffer overflow

Ep 256Episode 256 - 9 bits of podcast, 8 bits of computing
Josh and Kurt talk about 8 bit computing. What sort of security lessons can we learn from the 8 bit world? More than you think. Show Notes Legend of Zelda Random Number Generation Green rocket flame SR71 leaked fuel How do Namibian Himbas see colour? Suptuple meter music
Ep 255Episode 255 - What if security wasn't joyless?
Josh and Kurt talk about what we can stop doing. We take a position of asking "does it spark joy" for tools and infrastructure. Everyone is doing something they should stop. Show Notes Does it spark joy?
Ep 254Episode 254 - Right to Repair Security
Josh and Kurt talk about the new right to repair rules in the EU. There's a strange line between loving the idea of right to repair, but also being horrified as security people at the idea of a device being on the Internet for 30 years. Show Notes EU right to repair repair.eu